Small Business Privacy Policy: Write It in Plain English
To create a small business privacy policy, document how you handle customer information, then explain those practices in everyday language. Customers should understand what you collect, why you need it, and what choices they have.
You don’t need legal-sounding sentences to build trust. In Pew Research Center’s 2023 findings, 61% of Americans said privacy policies were ineffective at explaining companies’ data use.
Start with your actual business practices and explain them in plain language. This supports transparency and helps readers understand how you handle data privacy.
Key takeaways
- Write your policy around the information and tools your business actually uses.
- Explain customer choices alongside collection, sharing, retention, and security.
- Make the policy easy to find, get legal guidance, and update it when practices change.
1. Identify which privacy requirements apply
Your location, customers, and business activities determine which privacy laws apply and whether your business has a legal requirement to post a policy. A small team doesn’t automatically mean you’re exempt.
Start with US federal and state rules
According to BBB’s privacy policy guidance, the FTC recommends policies for most websites that collect and share consumer data. That isn’t a universal federal requirement for every website.
Federal notice requirements apply in defined situations. COPPA covers certain online services collecting information from children under 13. HIPAA requires privacy notices from covered entities in specified circumstances. The Gramm-Leach-Bliley Act requires notices from covered financial institutions.
State laws add requirements. CalOPPA broadly requires covered commercial websites collecting California residents’ personal information to post a conspicuous policy. CCPA, as amended by CPRA, has separate coverage criteria; not every small business qualifies.
Consider international customers and service terms
Different data protection laws may apply when you serve customers across jurisdictions. GDPR can apply when a business outside Europe offers goods or services to people in the EU or monitors their behavior. Personal data can identify someone directly, such as by name, or indirectly, such as through an online identifier. Canadian commercial activities may fall under PIPEDA or provincial laws.
Third-party contracts matter, too. Google Analytics’ terms require an appropriate privacy policy, while AdSense requires privacy disclosures. Include Amazon Associates links and Facebook Page connections in your inventory of services.
Use the FTC’s privacy and security resources as an official starting point. Get qualified legal advice about the rules attached to your operations.
2. Map the information your business collects
Before writing, trace the personal data your business collects through each customer touchpoint. Include your website, booking system, paper forms, store transactions, email inbox, and connected software.
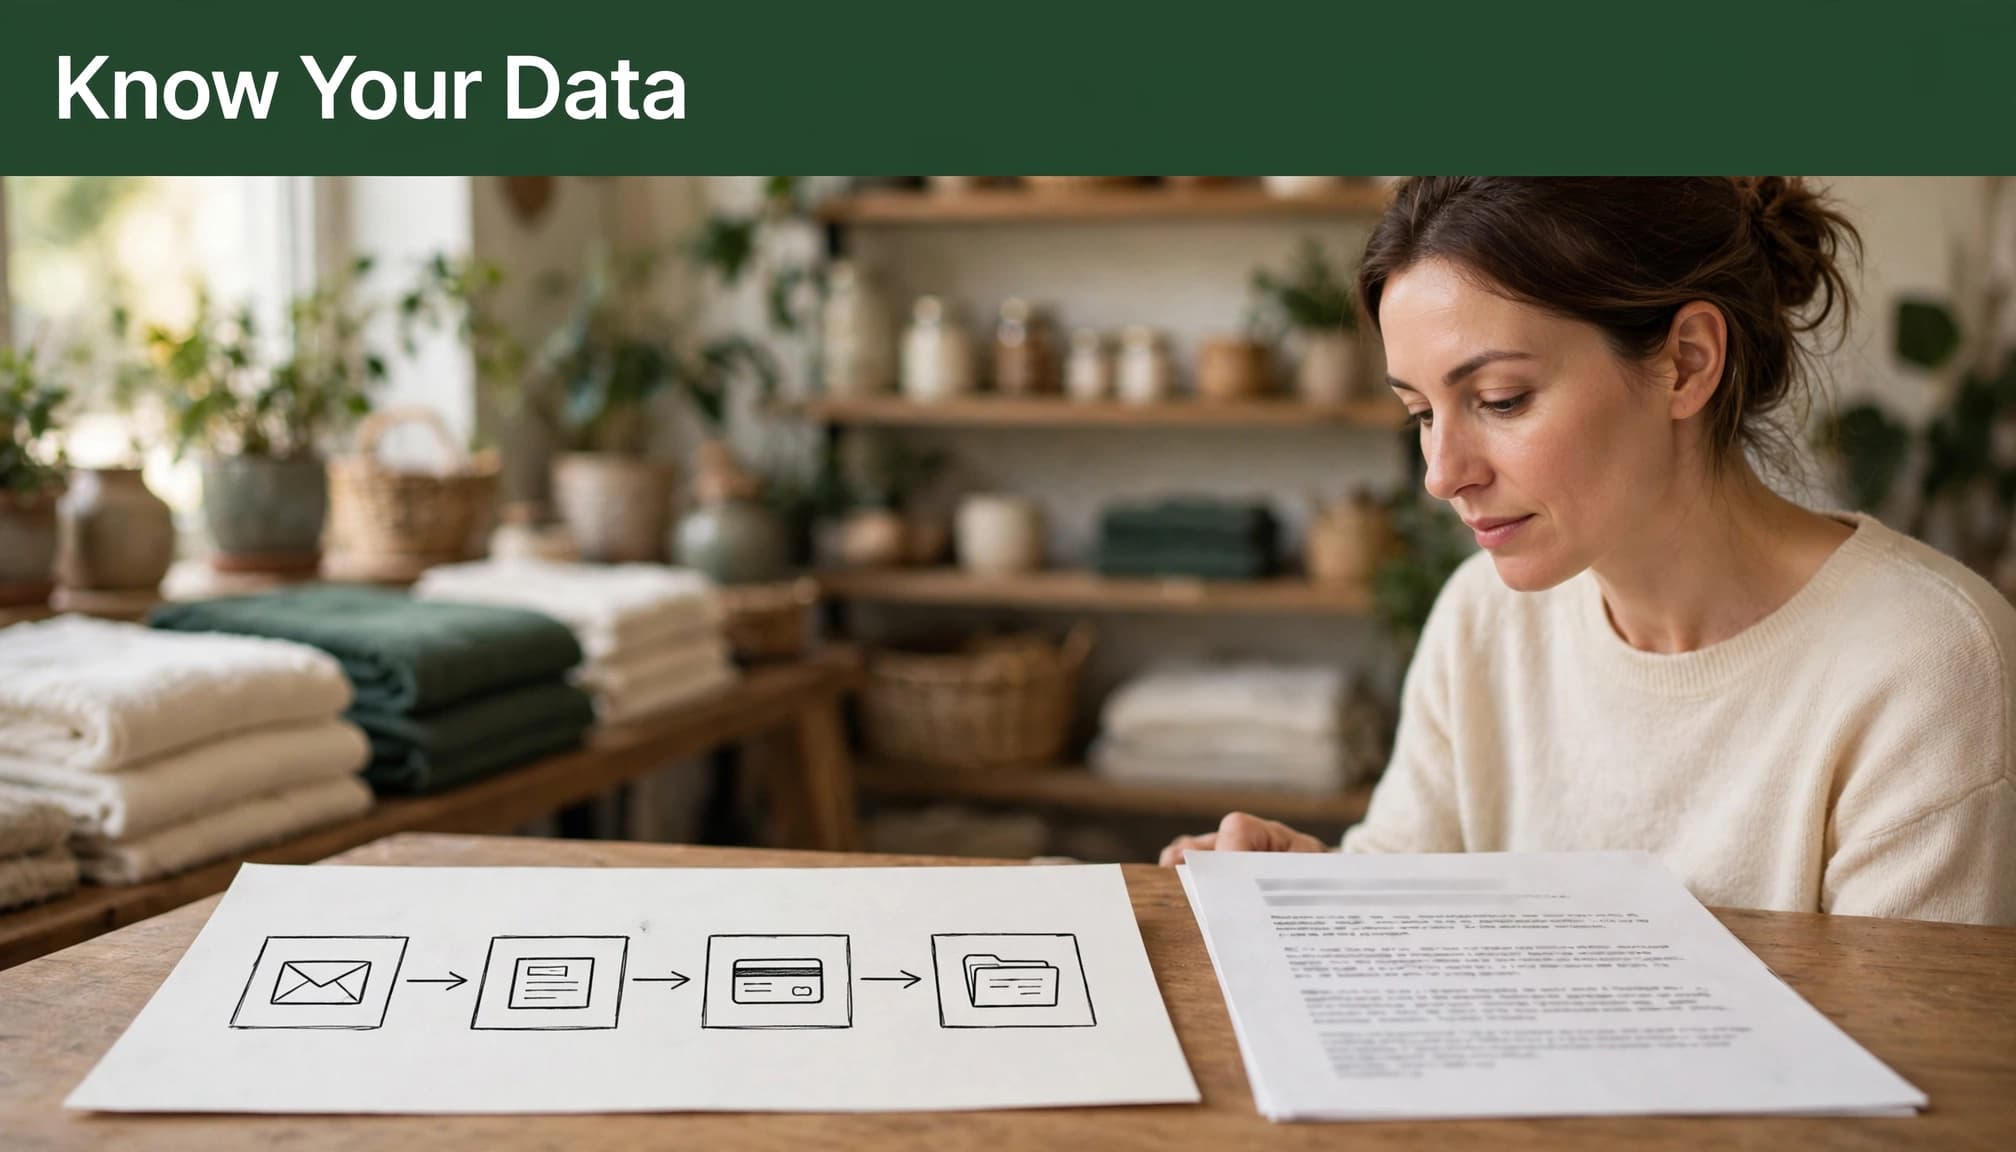
Use a simple inventory to capture what happens at each collection point.
| Collection point | Information to identify | Where it goes |
|---|---|---|
| Contact form | Names, email addresses, message contents | Inbox and form provider |
| Newsletter signup | Email addresses, preferences, consent records | Email platform |
| Checkout | Order details, addresses, payment information | Store, processor, shipping provider |
| Website tracking | Device information, IP addresses, browsing activity | Hosting, analytics, advertising tools |
Record who can access each category, which third-party services receive, store, or process it, and when you delete it. Distinguish information your business stores from information a payment processor handles directly.
Our website essentials for solo businesses can help you connect these decisions with your forms and booking process.
Collect only what you need. A general inquiry form rarely needs someone’s birth date or financial details.
3. Draft your small business privacy policy
Use this privacy policy template as a structure, then adapt every sample sentence to your actual practices before publishing.
Identify your business and explain collection
Begin with your legal business name, any trading name, and the policy’s effective date. State whether it covers your website, app, in-person transactions, or all three.
A scope statement could read: “This policy explains how we handle information when you visit our website, contact us, or buy from us.”
Next, name the information you collect and its source. For a contact form: “When you send an inquiry, we collect your name, email address, and the information you include in your message.”
Also describe automatic collection and information received through other organizations. Avoid catch-all phrases such as “any information we consider necessary.”
Connect each use with its purpose and recipients
Explain why you need each category. For example: “We use your delivery address to send your order and your email address to provide order updates.”
Describe sharing just as directly: “We share delivery details with our shipping provider so your order reaches you.”
Name key third parties or clear recipient categories. Cover advertising, analytics, legal disclosures, and any sale or sharing that requires additional disclosures.
For GDPR-covered processing, add legal bases, relevant international-transfer safeguards, complaint rights, and required contact roles. Covered CCPA businesses also need the applicable category and rights disclosures.
4. Describe retention, cookies, and security honestly
Check how outside providers handle retention, tracking, and security before relying on third-party services.
Explain how long you keep information
Give a retention period when you have one. Otherwise, explain the criteria you use instead of saying information stays “as long as necessary.”
For inquiry records, a starting clause could read: “We keep inquiry information while responding to you and resolving related questions, then delete it under our retention schedule.”
Your internal schedule should assign actual periods by record type. Address legal recordkeeping duties and backup deletion separately. Don’t promise immediate deletion if your systems can’t deliver it.
Explain cookies and tracking choices
Separate cookies needed for basic site functions from analytics and advertising tools. Identify their purposes and explain how visitors change their choices.
A purpose statement could read: “We use analytics tools to understand which pages visitors use and improve our website.”
Then describe the controls your site actually provides. Where consent is required, optional tracking must wait until visitors opt in. A policy alone doesn’t obtain consent.
Google AdSense’s required disclosures address third-party advertising cookies and users’ options.
Describe safeguards without exposing systems
A plain-language clause could read: “We restrict access to customer information and use safeguards appropriate to the information we handle.”
For data security, use HTTPS, unique passwords, multifactor authentication, software updates, and limited staff access.
Promise only safeguards you actually use. Never guarantee complete security or publish details that could help someone attack your systems.
5. Make customer choices and contact details usable
A customer-friendly policy explains what people can do, not simply what your business does.
Explain permission, opt-outs, and other rights
Give direct instructions: “You can opt out of marketing emails by selecting Unsubscribe in any newsletter.”
Keep newsletter permission separate from an inquiry or purchase. Ask people to opt in to marketing emails separately. Where consent supports processing, explain how people can withdraw it. Also describe applicable access, correction, deletion, portability, and sale or sharing opt-out rights.
These rights vary by law and can have exceptions. Explain any identity-verification steps without requesting unnecessary sensitive information.
For subscribers, record the signup date, source, consent wording shown, preferences, and later changes. Our guidance on email consent and preference records supports that routine.
Provide a monitored contact route
Identify the business responsible and publish monitored privacy contact information, plus other contact details required by applicable law.
A contact clause could read: “Contact us using the privacy email address below to ask about your information or submit a privacy request.”
Assign someone to log requests, locate records across providers, and respond within applicable deadlines. Explain lawful retention exceptions when responding to deletion requests.
Maintain unsubscribe suppression records where appropriate so a future import doesn’t restart unwanted marketing.
6. Publish, review, and maintain your policy
Put a clearly labeled link to the policy in your footer and beside contact, signup, account, booking, and checkout forms. GDPR requires accessible privacy information, and CalOPPA requires conspicuous posting.
Publish readable HTML rather than offering only a PDF. Use descriptive headings, good contrast, and links that work with a keyboard and on mobile. For apps, include an accessible in-app link and the required store-listing link.
Before publishing, use this review checklist:
- Every collection point, provider, and data use appears accurately.
- Retention rules and customer choices match your systems.
- Contact routes, unsubscribe links, and privacy controls work.
- A qualified legal reviewer has assessed the policy and its promises.
A privacy policy template gives you a starting structure, while a privacy policy generator such as TermsFeed can organize a first draft. However, neither can discover an analytics tag or newsletter automation you forgot to disclose.
Add the effective date and keep previous versions privately with a short change log. Review the policy and update privacy policy details whenever you introduce a tool, collection field, or sharing arrangement.
Covered CCPA businesses must update required disclosures at least every 12 months, under the California privacy statute.
Notify customers before substantial changes to data use or sharing take effect, using email, a prominent website notice, or another clear method. Obtain fresh consent where required.
Frequently asked questions
Do I need a policy if my website doesn’t take payments?
Possibly, yes. Contact forms, newsletter signups, booking tools, analytics, and advertising can collect personal information without a sale.
Your legal duties depend on applicable laws and your practices. Service contracts can also require a policy, so a brochure-style website isn’t automatically outside privacy requirements.
Can I copy another company’s policy?
Don’t copy another business’s policy. Its providers, collection practices, retention periods, and legal obligations may differ.
Use a template for structure, then write around your own inventory. Because your business is responsible for its privacy promises, get legal guidance before finalizing the document.
Build trust with promises you can keep
A useful privacy policy gives customers clear expectations about their information. Its wording should match what happens in your forms, software, and daily routines.
Start with your data inventory, turn each practice into plain language, and arrange legal review. Clear expectations and promises your business can keep support customer trust.